
Chains in Sweden, Belgium and Luxembourg say fridge temperatures rose overnight, similar to hack of French stores
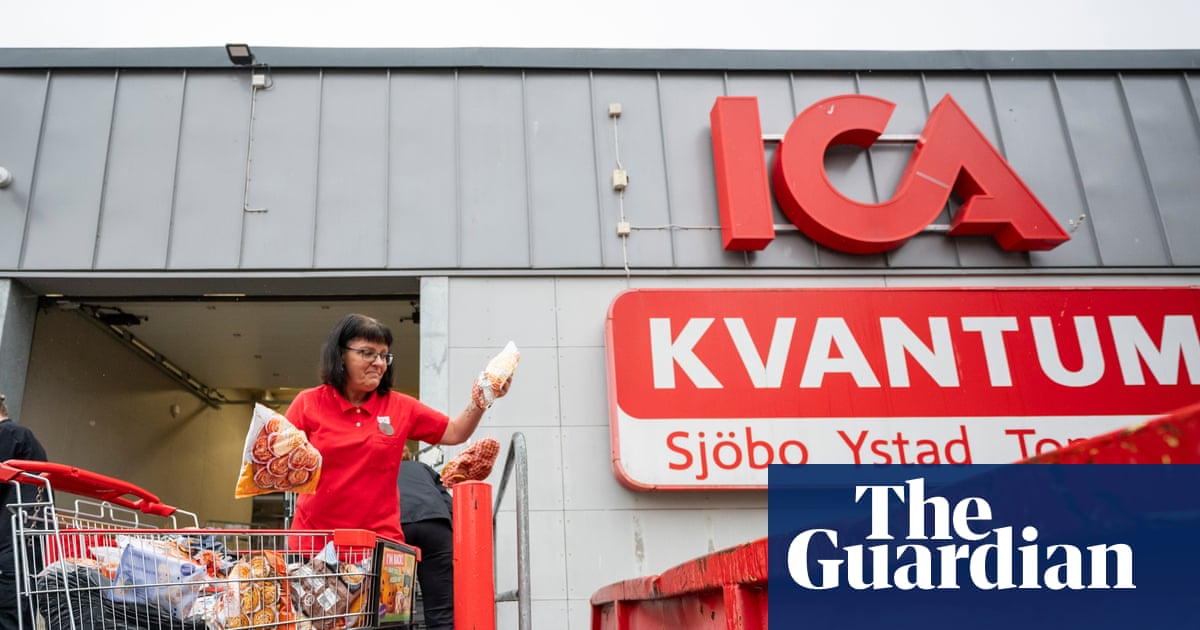
Supermarket chains in Sweden, Belgium and Luxembourg have said the temperatures of their refrigerators and freezers in dozens of stores rose overnight, prompting fears of a cyber-attack similar to one that caused millions of euros of food losses in France.
Sweden’s Coop chain told the daily Aftonbladet on Monday that six of its stores had been affected, while ICA said it was “aware that a limited number of stores were affected by an incident overnight which impacted their refrigeration and freezer systems”.
deleted by creator
Stop connecting shit to the internet, this is not a difficult problem to fix.
I was gonna argue that a local remote control alternative doesn’t exist, but I really don’t know why you’d need freezers to be remotely controlled. They’re more of a set and forget.
Walmart had that since the early 2000’s. Fucking bullshit then too. We once had a section go out and called corporate and they argued it was working because their computer said so. Fucking dumb asses we are looking at it and some asshat in Arkansas (we are in Texas) tells us we are wrong. They finally agreed to send a rep from headquarters to drive down and look for himself (who knows cost of that) just for that guy to go "yall right it broke. " Then.we got local guy come fix it.
But god forbid someone take a package of baby formula
At a large scale you want some settings to monitor temps and controling defrosting and cleaning. I’m sure energy management is also helpful if there is a power cut or the backup generators are taking a minute out two to warm up.
👏Stop 👏 making 👏 everything 👏 connect 👏 to 👏 the 👏 internet👏
Why these on network with outside access?
Because stupid. There’s zero reason for them to be on the public internet beyond incompetent operational IT security.
Exactly ; the concept itself is the real flaw.
In theory they gather all sorts of data so they can see how efficiently they’re running, whether maintenance is needed. If something goes wrong with one of the units they can dispatch a repair guy immediately, or have the store shift the food before any spoilage. If they’re smart about it they can use the data to set up an efficient preventative maintenance schedule and really stay on top of things.
A chain that has 500 stores with 20 units a piece adds up fast. They probably have a person at headquarters whose only job it is to stay on top of these units.
You do that with your own internal network or, at max, with a vpn. You don’t need them to connect to the internet at all.
Yup, absolutely correct.
Automation engineer here, this is 100% a problem with their network model
No reason not to connect to the internet. Put the units on their own VLAN and firewall that off from anything but the IP of the monitoring end. Plenty of other ways to make this secure, that one’s off the top of my head.
Exactly why do you need to do this instead of just keeping everything out of the internet and then connecting through a vpn tunnel?
If you need to monitor these 24/7 for some reason, pay a department that works 24/7 locally. Otherwise is just half-assing solution that will end like this sooner than later.
No reason at all to connect any kind of sensitive machinery to the internet, especially if remote operation of it can cause harm or damages.
pay a department that works 24/7 locally
AH! I don’t think you have an idea of how much even a minimum wage employee actually costs. Whatever you think, double it. $15/hr.? OK, that’s $30 cost to the company.
And then you lose the ability to manage and collect data centrally. You could have a couple of dude likes me sitting at home in shifts, monitoring a thousand locations, putting in tickets for issues and submitting fancy charts to corporate. And you want 3,000 dudes like me on site in shifts? Yikes.
Point being, securing a device on the internet is child’s play. There’s simply no excuse not to do so. Even the dumbest SOHO router allows one to control a firewall. Aside from labor, setting up a corporate VPN for this use case would cost beans. I’m dumb and I can, and have, done this.
Wow… where do I start?
If the department is that important, you pay people to have it manned 24/7. Yes, despite the cost, because it’s that important. Where I work, we have an NH3 cooling system and it is that important, so it’s manned 24/7 locally. But I digress…
You can collect that data locally, in a machine that is only reading the data (not writing it) and that then relays it to the outside through a VPN to which are connected only the relevant people. That way the machine is kept local, but gives your central the data it asks for. Again, no need for a freezer to be connected to the internet at all.
Then, to keep it local and safe, if you don’t want to pay someone 24/7 what you do is set a series of setpoints to trigger warnings and alarms that will notify your local team (which, even if it’s not 24/7, should be on call) to intervene in case of need. That way, if your freezer temps raise above the threshold, your local team will get a call automatically and act before even the central knows.
But ok, let’s say you, for some absurd reason, need to micromanage the freezers of the whole country from the central offices. If that’s the case, and I guess you have a good bunch of freezers to manage then, what you do first and foremost is creating a VPN to connect them all. And with that done, you allow access to it only to a controlled set of devices from which you can manage the freezers and that is separated from your administrative network to keep it safe.
And yes, all this costs money, but if you are big enough to be a target, you should be spending in security because the bigger you are, the bigger your loss when an attack happens. Looks to me that you’re just trying to save poor corporate some money by cutting corners when it comes to security and well… that’s a valid strategy… until you’re targeted.
That one’s not very secure.
Why not? Firewall off that VLAN and it doesn’t exist to the outside world. Port scan the supermarket IP (how did they get those?) and you’ll see nothing. Only way in is to hack all those routers, and if there’s a mix of brands and models, that just got way more complicated. Then you have to proceed with the attack.
Because spoofing. More complicated for sure but an attacker with knowledge of the layout could get some data through in some typical setups. Stop messing about and vpn or airgap it, if you want any sort of secure.
Maybe we should stop putting appliances on wifi? Like, for everyone everywhere?
It’s worse. They were connected by 4G.
I work for the food industry, in automation. Our whole factory is connected. To the point that from my office, I can control most of the factory machines. From my office, from my laptop that needs to be connected through an ethernet cable to one of the tech network of the factory.
If I want to connect from another device, I need to set up a vpn with credentials and an authorised IP.
The only way to access our tech network from the outside is stealing my credentials and then ask some of my colleagues to authorise a device and IP for my credentials, something highly suspicious that would raise a lot of alarms.
I’m not going to say that a system like this is infallible but turns an attack like this extremely unlikely. This is how you should have your systems “connected”. Not through a login portal exposed to the damn internet.
Thanks I’m now in your system
Oh shit! While you’re in, can you please check my email and maybe answer some so I don’t have to tomorrow?
Thanks in advance!
YTF does a refrigerator need to be on net control??? Isn’t it a set once and forget it device? Maybe to monitor it to report a failure… but to CONTROL it???
It’s more convenient for the hackers this way, duh
it’s so they can sell subscriptions to the cloud bullshit.
They had their warning from similar attacks a few weeks ago. Whoever was stupid enough not to pull the plug on this interface deserves the losses. From the costs for the freezer contents, they could have hired even a pricy security specialist.
Apparently the Swedish freezers were scheduled for updates for tomorrow, Wednesday. I guess too little, too late.
The Irish supermarket impacted only had 13 nationwide.
Based on their stock management they probably didn’t even know they had them 😂
imagine having a freezer that’s susceptible to a cyber attack. Why the fuck is it connected to the internet? All it needs is a thermostat. The closest thing to a “smart feature” that might benefit is the ability to send a notification if power fails or temperature falls below a set value, neither of which should be hackable by an outside party.
Even then, you can just have a battery powered thermometer connected for alerts. These have been available for a decade or more. No need to have the fridge involved at all…
To warn the technical department when the temperatures start rising and something is wrong. Sellers would not really pay attention to some fridge or freezer being warmer.
There are four ways of doing that:
- people on site
- an internal network that can only be checked locally
- proper supervision network that can push its state outside, but not be altered from the outside
- whatever the fuck they did
Guess what option was picked.
That’s a great reason to be on an internal network, but it surely doesn’t need to be on the internet.
I mean, part of my job as a stocker of the frozen and refrigerated foods was checking to make sure the fridge and freezer’s temps were within spec every time I entered them, and to report if it was too warm or cold so it could be fixed.
Not to mention alarms and other ways of indicating issues. There could easily be a one-way signal that is inaudible to customers for example.
Yeah, there are a lot of things I’m supposed to check at work too
Right!? Haven’t we had these solutions for commercial fridges/freezers for quite a while now? Why on earth did we bring the internet into it? 😅
Stop fucking connecting everything to the stupid internet. Everything should be offline first.
The current way is if it can be connected to the internet, that must be done, it must be an advantage. Ditto with AI. People need to chill and realize that not everything benefits from this shit and sometimes you even worsen the product/service ffs. Just stop!
You mean to tell me that none of these people thought to disconnect them the first time?
It was on the agenda for the next quarterly interdepartmental meeting, and after that needs a cost estimate and budget approval to actually start working on the issue.
Maybe not everything needs to be on the internet.
I think these fridges are only supposed to be on the local network so they can be controlled centrally, and I assume the attackers gained access to the network. I HOPE these aren’t connected to a Datacenter like those cheap Chinese smart lights
Oh im willing to bet they are connected outside in someway. How else is the company gunna sell a subscription for fridges?
OP’s name checks out.
The question isn’t so much, “Why were these on the internet?”, so much as, “Why were these not securely connected?”
At my last job, our AWS resources were firewalled off, only accepting connections from our internal VPN. To get on that, you had to be coming from the IP of an office or a DevOps team member’s home IP.
The local firewalls could have only allowed traffic to the freezer VLAN from the remote monitoring IP.
And that’s just two ideas off the top of my head. If my dumbass can do it, you don’t need a high level networking expert to fix this.
I work as an IT consultant, and this doesn’t surprise in the least. Non-tech companies tend to have terrible security posture and governance. It seems like they only implement a basic security posture if they have to by law or they got hacked and lost a lot of money. I think the unintended consequences of this hacks are actually helping supermarkets to get their shit together in cyber security
Yep! But this was the second such attack. I get being stupid the first time around, totally understandable.
Looks like people didn’t learn any lessons from the past cyber-attack. Well, these kinds of attacks will continue as long as users don’t take corrective measures !
Just unplug them… Decouple them from wifi